PDI-P Faction in DPR Agrees to Pursue Statement of Opinion Regarding Gibran
-
News
-
2 minutes ago
This article was translated by AI. Read the original article on Kompas.com. See Original
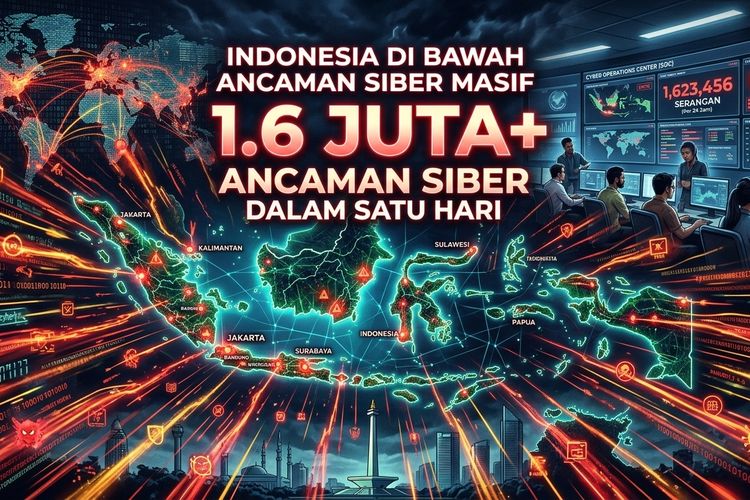
"We request that OJK take immediate action to establish a cybersecurity monitoring center. Large banks have their own budgets and experts, while BPRs and regional banks do not. We believe regulations should not allow BPRs and regional banks to face cyber threats without state protection," said Hasanuddin in a statement on Wednesday (11/11/2026).
Hasanuddin pointed out that BPRs and regional banks are among the most vulnerable groups.
This vulnerability arises from the limited resources of these banks, making it challenging for them to develop independent cybersecurity defense systems.
"Hackers no longer target their victims based on the size of banking assets. Banks with weak defense systems may become gateways to attack the interconnected financial ecosystem," he stated.
He revealed that an attack on regional banks occurred in late 2025 when a vulnerability in the BI-FAST service of several BPDs was exploited by hackers for illegal transfers, resulting in estimated losses of up to Rp 200 billion.
Furthermore, in Financial Services Authority Regulation No. 34 of 2025, OJK acknowledged that the information technology management in the BPR and BPRS industries remains vulnerable to cyber incidents.
Hasanuddin appreciated the steps taken by OJK and Bank Indonesia (BI) to activate the Cyber Incident Response Team (TTIS) since November 6, 2026. However, he stated that this emergency measure must be followed by more systematic long-term policies.
He outlined three steps that could be taken. First, OJK should establish minimum cybersecurity standards applicable to all banks, regardless of their scale of business.
Second, it should strengthen direct information exchange regarding cyber threats between OJK, BI, and the National Cyber and Encryption Agency (BSSN).
Third, banks must be required to notify customers within 24 hours of any data breaches and ensure the return of customer funds if losses are proven to result from bank system failures.
"However, we request that enhancements to cybersecurity should go hand in hand with public education, especially for micro, small, and medium enterprises (MSMEs), market traders, and farmers who increasingly rely on digital transactions," said the Secretary General of the National Awakening Party (PKB).